People and roles
Three roles, what each can do, how they apply to the builder as well as to the buttons, and why they belong to a workspace rather than to an account.
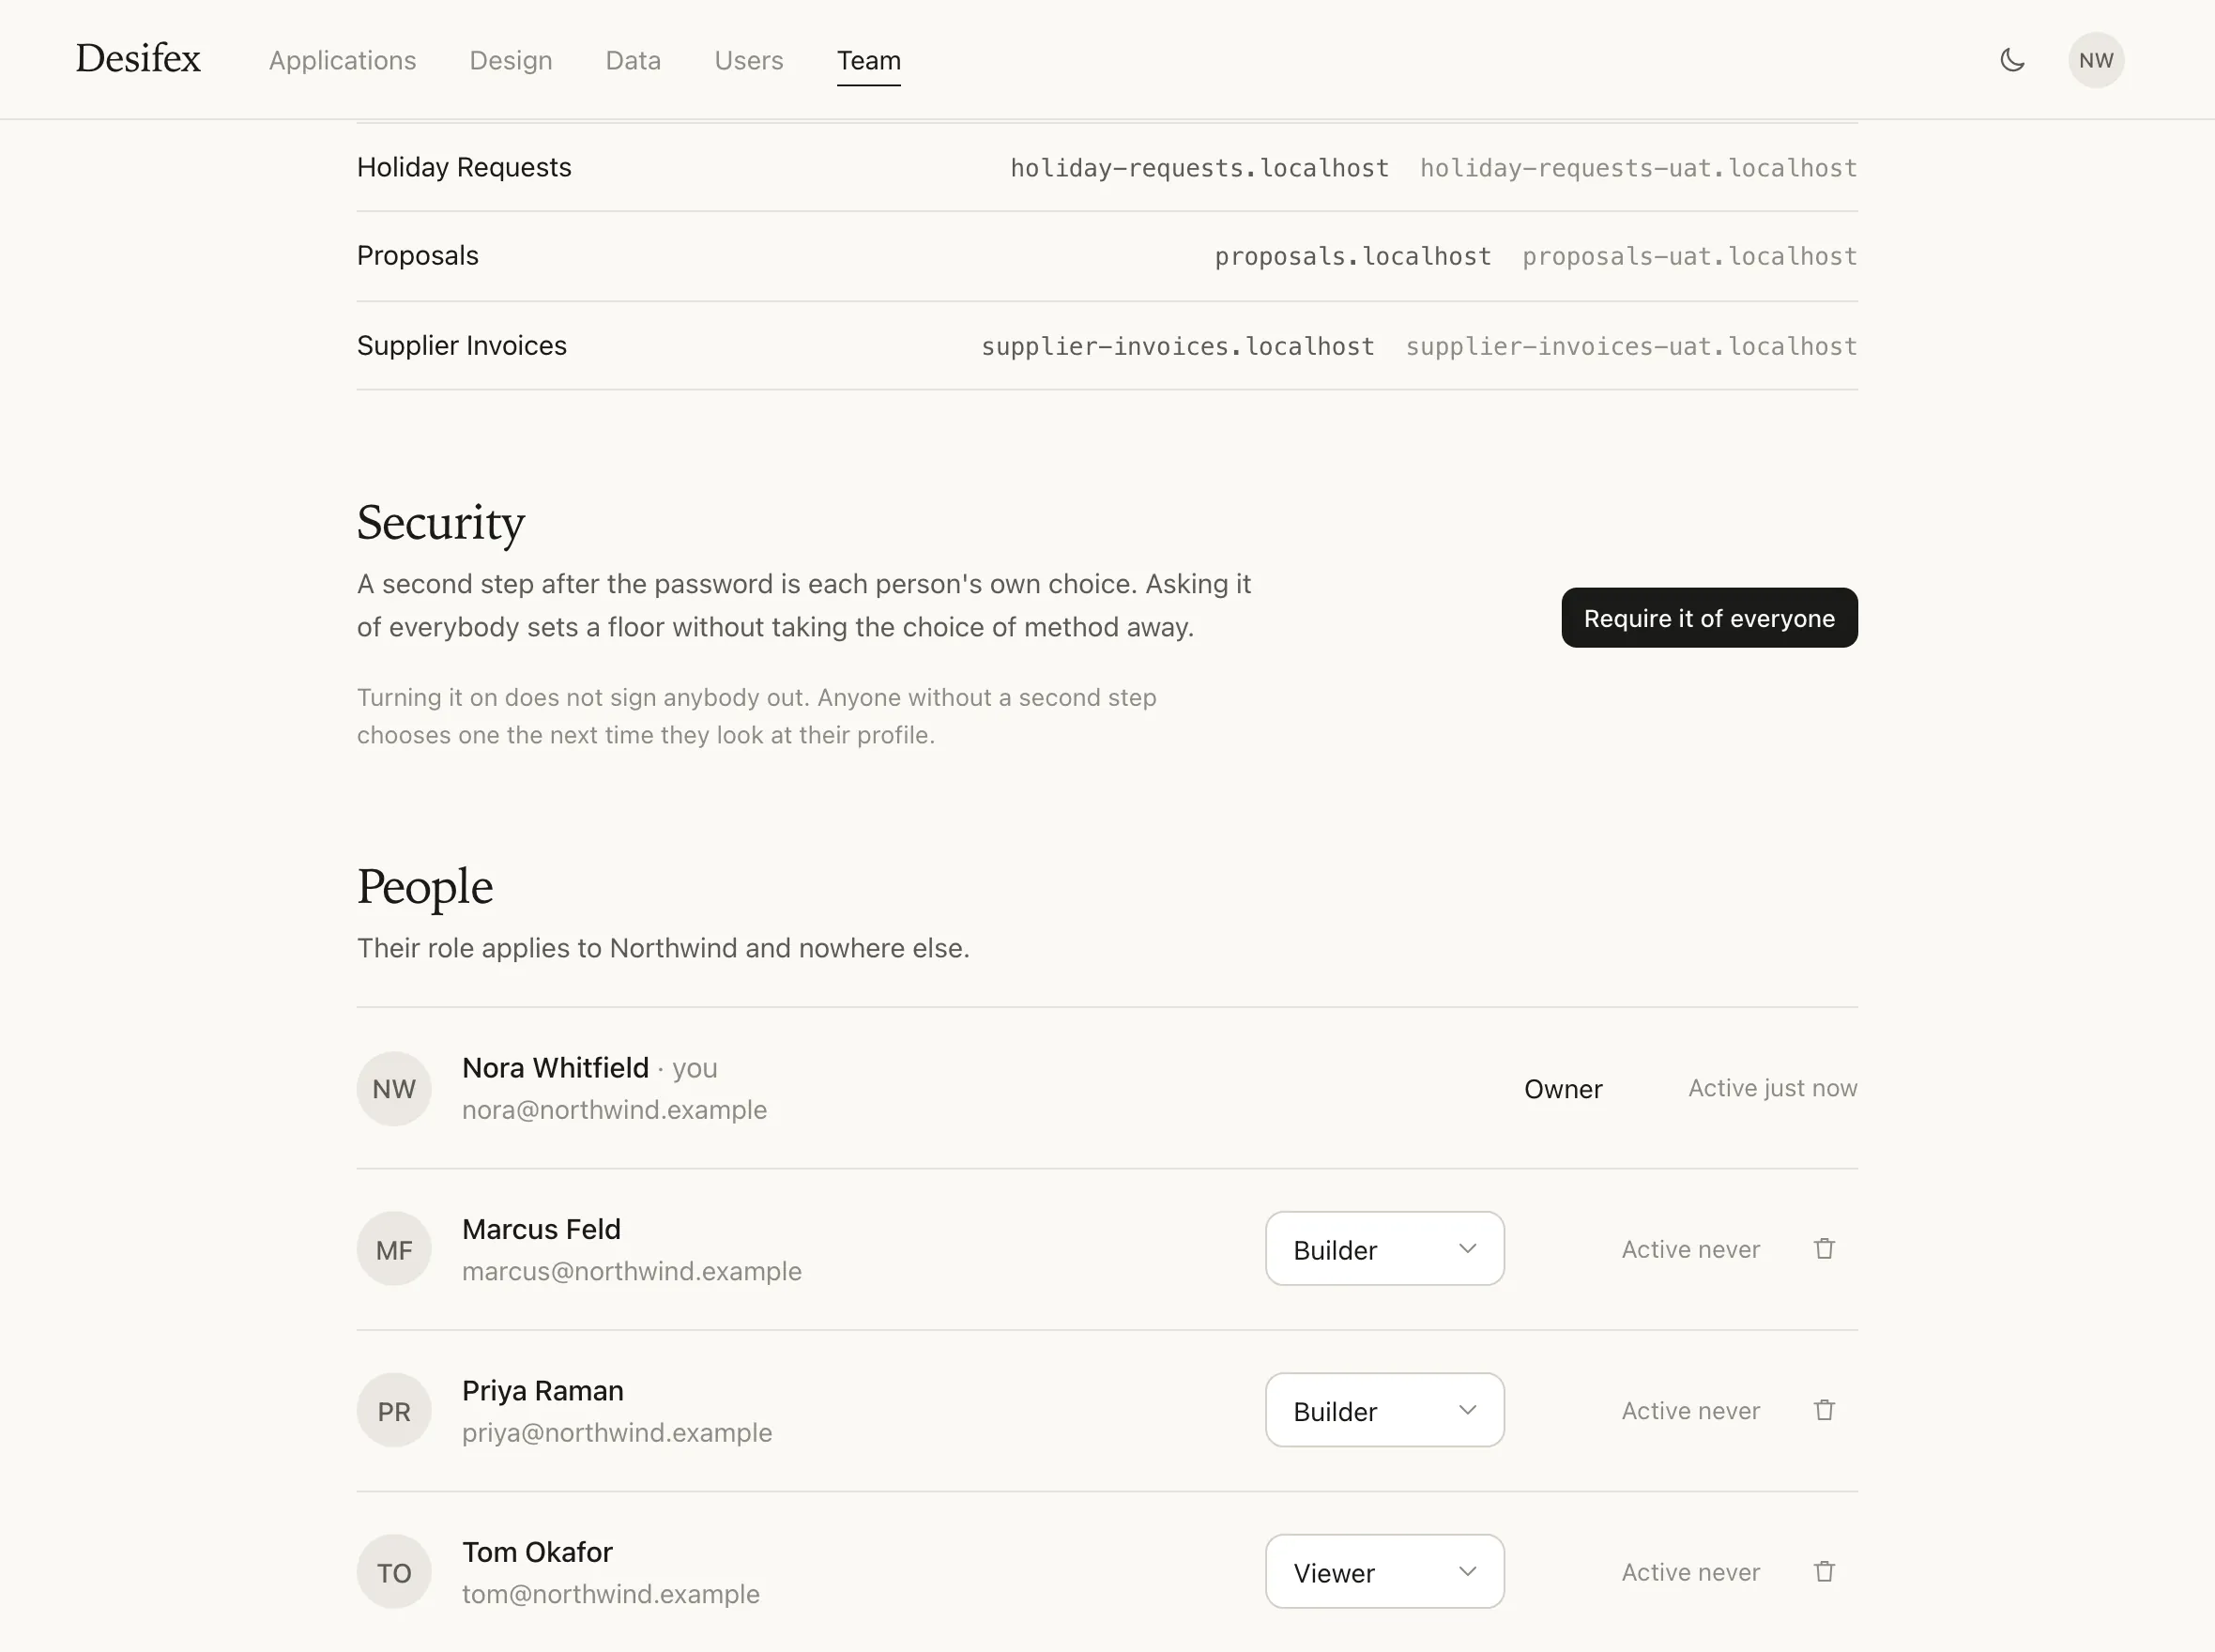
Three roles. Each person in the workspace has one — in this workspace. Somebody in more than one holds a role in each, and they do not have to match.
| Role | Can |
|---|---|
| Owner | Everything below, plus managing the team, renaming the workspace, setting its domain, deleting applications, clearing out an application's data, and downloading the source |
| Builder | Create applications, direct the builder, save versions, deploy, publish files, add and correct records |
| Viewer | Read applications, previews and what they have stored. Nothing that changes or ships anything |
Choosing one#
Viewer for somebody who needs to see what is being built — a stakeholder, a colleague in another department, a client if you have given them an account.
Builder for anybody doing the work. This is most people.
Owner for the small number of people who should be able to delete things, change the workspace domain, and take the source away.
The roles apply to the builder too#
This is the part worth understanding.
When you ask the builder to do something — deploy, add a user, connect a domain — it acts as you. Your role is resolved and enforced in exactly the same code the buttons go through.
So a viewer cannot deploy by asking nicely, and an owner-only action stays owner-only however it is phrased. There is no way round the roles through the conversation, which is the point.
Adding somebody#
An owner presses Add teammate on the Team page and gives an email address, a name and a role.
If that address already has an account — because they work in another workspace, perhaps yours and a client's — they join this one and keep the password they already had. Nothing is sent to them.
If the address is new to the platform, there are two ways in, and the dialog asks which.
Email them an invitation#
The default, and the one to use. They get a message with a link, they choose their own password, and they are signed in the moment they have.
The link works once and expires after seven days. If it is used, lost or left too long, ask an owner to add them again — that issues a fresh invitation and retires the old one. Only one invitation for a person is live at a time.
The password is chosen by them and stored as a hash, so it never exists anywhere but in their head. Nobody at your workspace, and nobody here, can read it back.
The same screen asks them who they are: their first and last name, what they would like to be called, a title if they want one, and a picture. All of it is prefilled from whatever you typed and all of it is optional — somebody who only wants in can press straight through. It is asked here because this is the one moment they are certain to be paying attention, and because the name you typed came from memory onto an account that did not exist yet.
Set a temporary password#
The fallback, for when mail is the problem: an address that bounces, a colleague standing next to you, a platform whose mail has not been set up.
You type a password of at least ten characters, or press Suggest one for three words and a number — readable aloud across a desk, which is the point. They are emailed it if mail is working, and they must change it before they can do anything else: the first time they sign in, the workbench puts them on their profile page and keeps them there until they have.
If the message does not go#
The account is made either way. Being unable to send an email is not a reason to refuse to add a colleague — so the Team page tells you the account exists and the message did not, and you can read them the password yourself or try again once mail is working.
Changing and removing#
Roles can be changed afterwards from the dropdown beside each person, and somebody can be taken out with the button at the end of their row. Removing them signs them out of this workspace at once and touches nothing else they have: their account, and any other workspace they are in, carry on.
The last owner#
A workspace with no owner cannot be administered by anybody, and there is no way back from that. So the only owner cannot be stepped down, removed, or leave of their own accord. Make somebody else an owner first, and then any of the three is fine.
Sessions#
Signing in creates a session that can be revoked immediately. Removing somebody from the workspace, or suspending them, signs them out at once rather than waiting for something to expire.
Anybody can add a second step to their own sign-in — a code by email, by text message, or both — from their profile. It is theirs to turn on and theirs to turn off; an owner cannot do either on somebody's behalf, because an administrator who can switch off a colleague's second factor is a way round it.
Requiring it of everybody#
An owner can ask it of the whole workspace, under Security on the Team page. Press Require it of everyone and nobody here can choose Off any more.
It sets a floor, not a method. Which channel somebody uses stays their own choice, because a method imposed on a person who cannot receive it is a person locked out. Turning it on signs nobody out either: anyone without a second step chooses one the next time they look at their profile.
What only an owner can do#
- Manage the team.
- Require a second step of everybody in the workspace.
- Rename the workspace and set its domain.
- Delete an application.
- Empty or delete a table, or empty a whole environment, on the Data tab.
- Remove somebody from the user directory.
- Download source.
That last one is deliberate: taking an application away in full is a considered act with a technical colleague in mind, not something to do by accident.